OAuth 2.0 is widely expanded along with the growth of social media networks these days
Written by Lê Trần Xuân Phương (XP) from Safewhere team
OAuth 2.0 is widely expanded along with the growth of social media networks these days since it is the most common technique behind the scenes to integrate social media login to an application that requires account registration.
When talking about OAuth 2.0, many people (developers too) think about the authentication, security or SSO thingies. Hence, let’s briefly look through web authentication mechanism history to reveal the truth about OAuth 2.0 before talking about its usages and how it brings benefits to your applications.
HTTP basic authentication
From a very old day, the simplest pattern, which is also the most familiar to everyone, is HTTP basic authentication. This is a simple challenge and less secure mechanism that a server can request authentication information from a user. Each web application has to manage to store or protect its own credentials database.
Federated identity and SSO
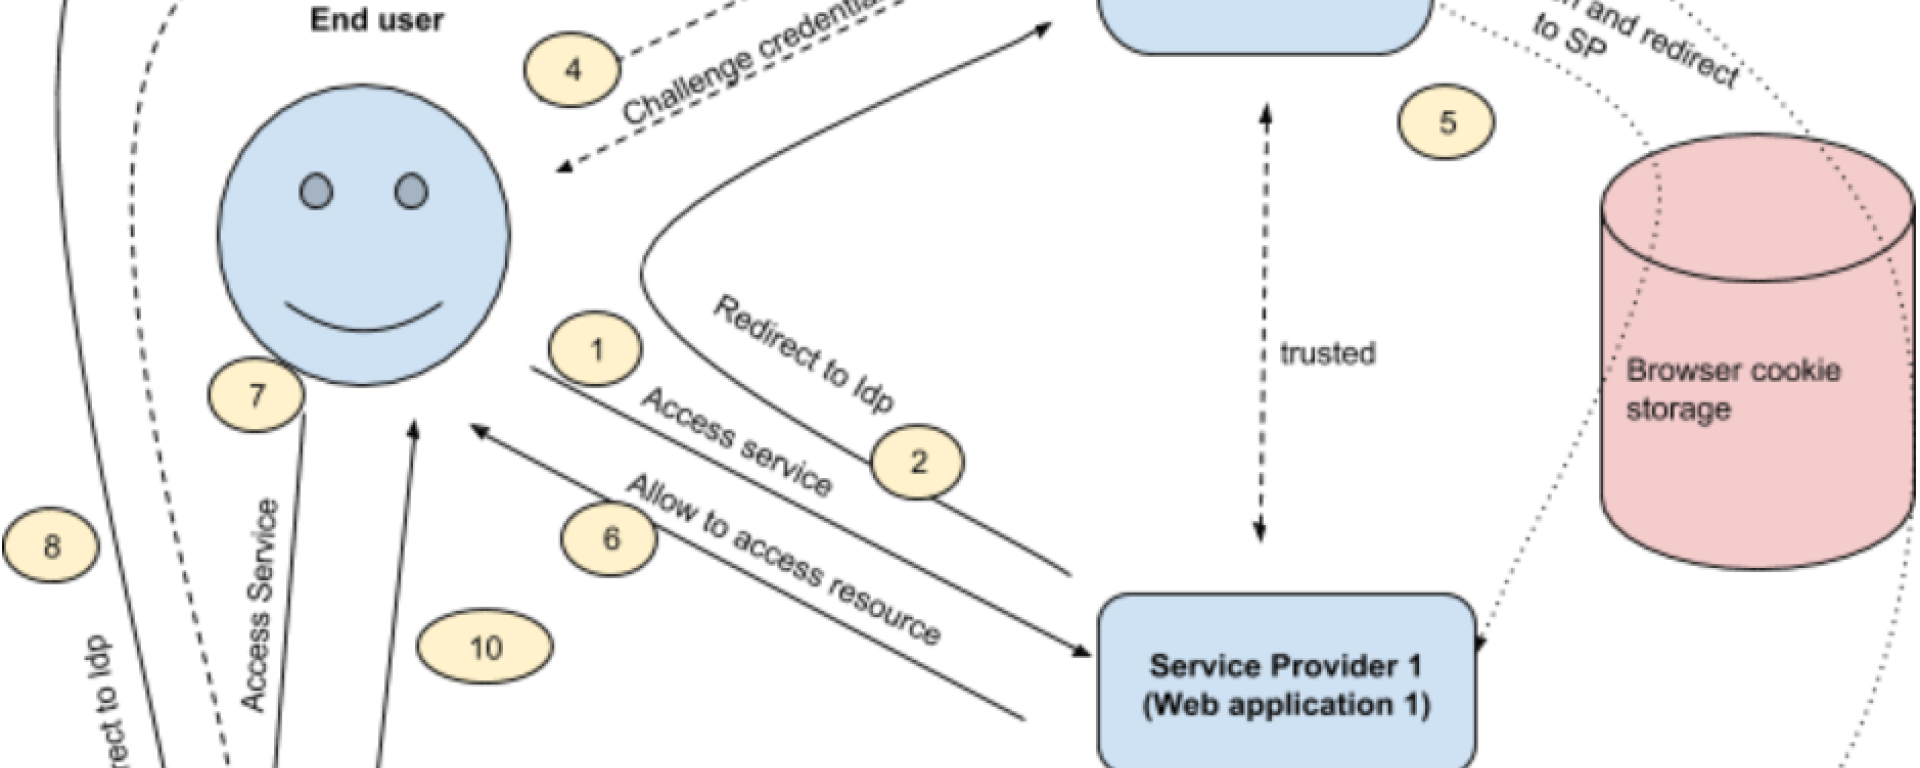
Time flies, the number of websites and services was rising rapidly, a user would want to access multiple sites at once. Federated identity concept and SSO on top of it were born as a revolution. In which, a web application (aka service provider or sp) is secured by an identity provider (aka idp). Firstly, the end user needs to contact the identity provider to negotiate a security token (known as cryptographically signed token) and then secondly hand it off to the SPs to access these sites. That means the web applications delegate the authentication and security matters to their idp. Hence, if a user is already authenticated, he/she will be allowed to access those sites’ resources without worrying about permission anymore, which is illustrated in the following image.
SAML
Another important note is that in the first years of the 21st century, most of the websites were heavy and their interaction happened on browsers only. That’s the reason why the first and the most popular specification for Federation/SSO was known as SAML 2.0, an OASIS Standard released on March 15, 2005. SAML 2.0 specification contains lots of open standards and one of which is specially designed for web SSO. It uses session cookie storage in web browser to keep user’s identity which contains identity claims and is signed by idp to access webapps. Hence, it would be a problem for using SAML 2.0 out of web browsers.
The modern web technologies Many years later, web technology has jumped to another stage. Now we have modern web, mobile, device-based applications and especially the expansion of social media networks (Facebook, Google, Twitter, etc.) which have different behaviors than the traditional web application. Instead of loading the whole application data from its own server, it tends to make AJAX calls to internal/external REST API service.
Authorization or Authentication
So does the way people build their web service. Now they prefer to use REST or stateless APIs than WCF service. For a common REST APIs service, it would be shared to a lot of applications as well as lots of different kinds of devices. As a result, SAML 2.0 significant advantages are not viable anymore in this situation. Using basic HTTP authentication is not a good option either since the service has to share user credentials around to many client applications. So, it turns into a question of how to give access to an application without giving it user’s credentials. That is about authorization matter, not authentication anymore.
That’s the time OAuth 2.0 became popular.
-Xuan Phuong-